
 Script Planner Assistant▸
 AI Apps
 AI News
DeepSeek Database Leak: Chat Records, Keys, Backend and Other Sensitive Data Exposed
小编 ·

DeepSeek Database Leak: Chat Records, Keys, Backend and Other Sensitive Data Exposed
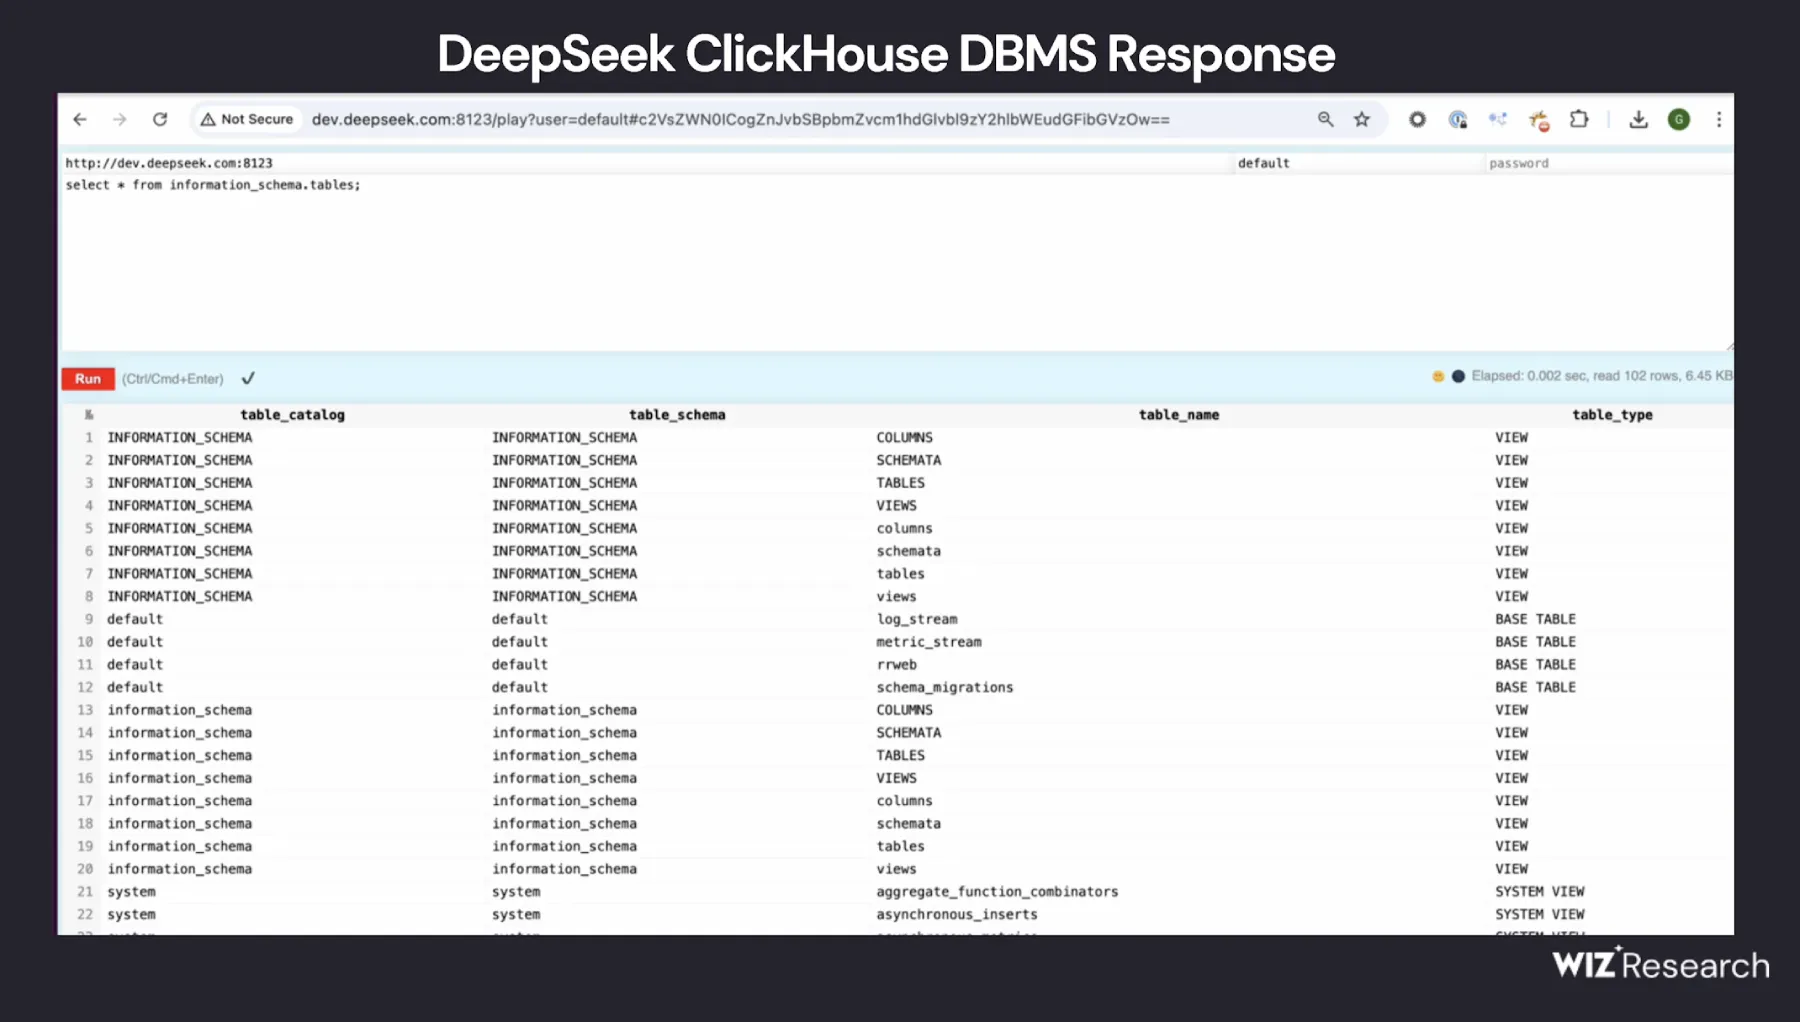
Wiz Research discovered a publicly accessible ClickHouse database belonging to DeepSeek, which allowed full control over database operations, including access permissions to internal data. The database contained a massive amount of chat history records, backend data, and sensitive information, including log streams, API secrets, and operational details.
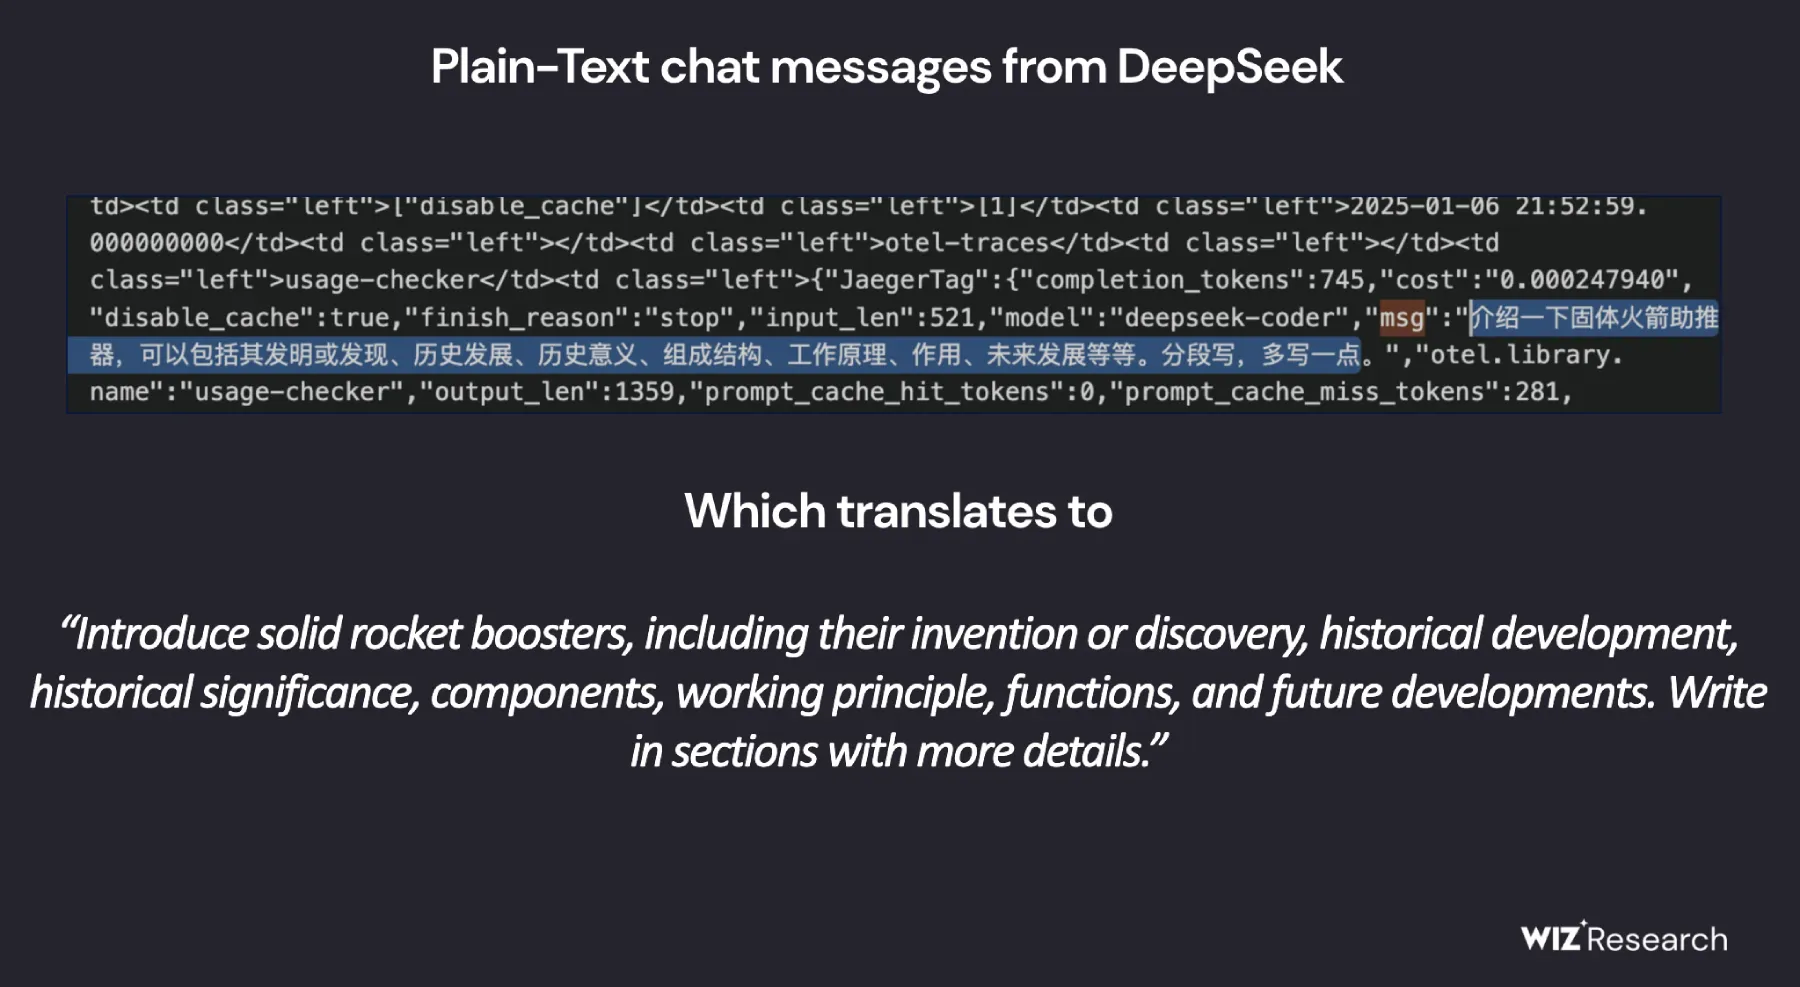
The Wiz team confirmed that this leak was not a hacker attack, but rather caused by a human misconfiguration: DeepSeek did not properly configure the database access permissions, and the port was exposed by default. This exposure allowed full database control and potential privilege escalation within the DeepSeek environment, with no authentication mechanism in place—anyone could access the database.
The WIZ research team promptly disclosed this issue to DeepSeek, and DeepSeek subsequently fixed the security vulnerability quickly.
Chinese AI startup DeepSeek has attracted massive media attention thanks to its groundbreaking AI models, particularly the DeepSeek-R1 reasoning model, which rivals OpenAI's O1, as well as for its cost-effectiveness and efficiency.









